Free field brief · November 5, 2026
What NYDFS examiners look for in your risk assessment.
The September 10, 2026 NYDFS industry letter in plain language: five common gaps examiners find in risk assessments, and five questions for your team.
Why it matters
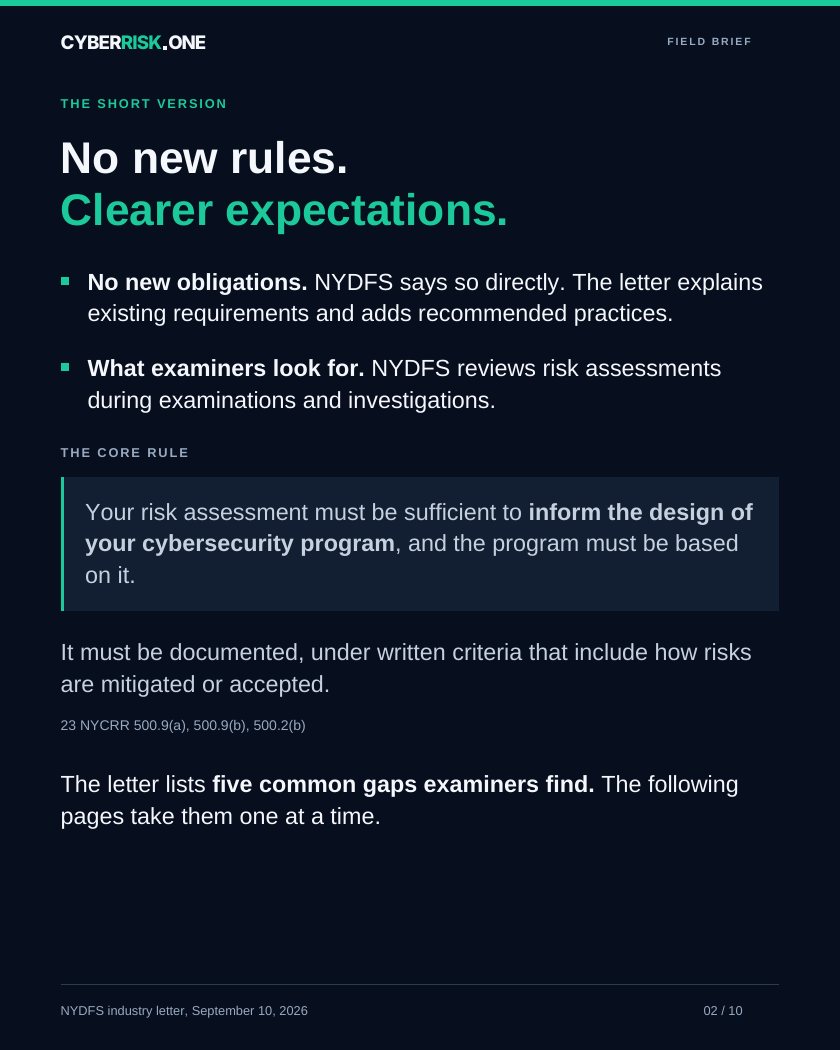
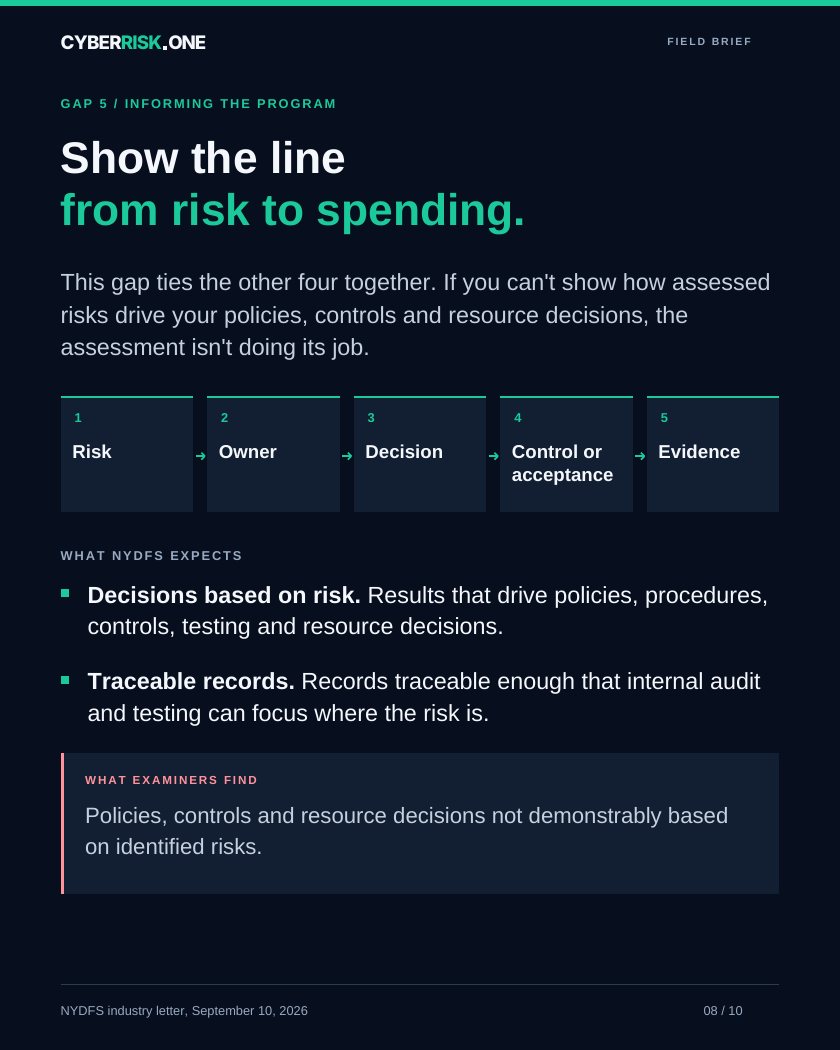
NYDFS reviews risk assessments during examinations and investigations, and its September letter says what examiners keep finding. It creates no new obligations. It explains what Part 500 already requires: a documented risk assessment that is good enough to shape the cybersecurity program, and a program that is actually built on it.
Source: NYDFS industry letter, September 10, 2026. A summary of public guidance in our own words, not legal or compliance advice.
What you'll learn
- The core rule in 500.9 and 500.2(b), in one sentence
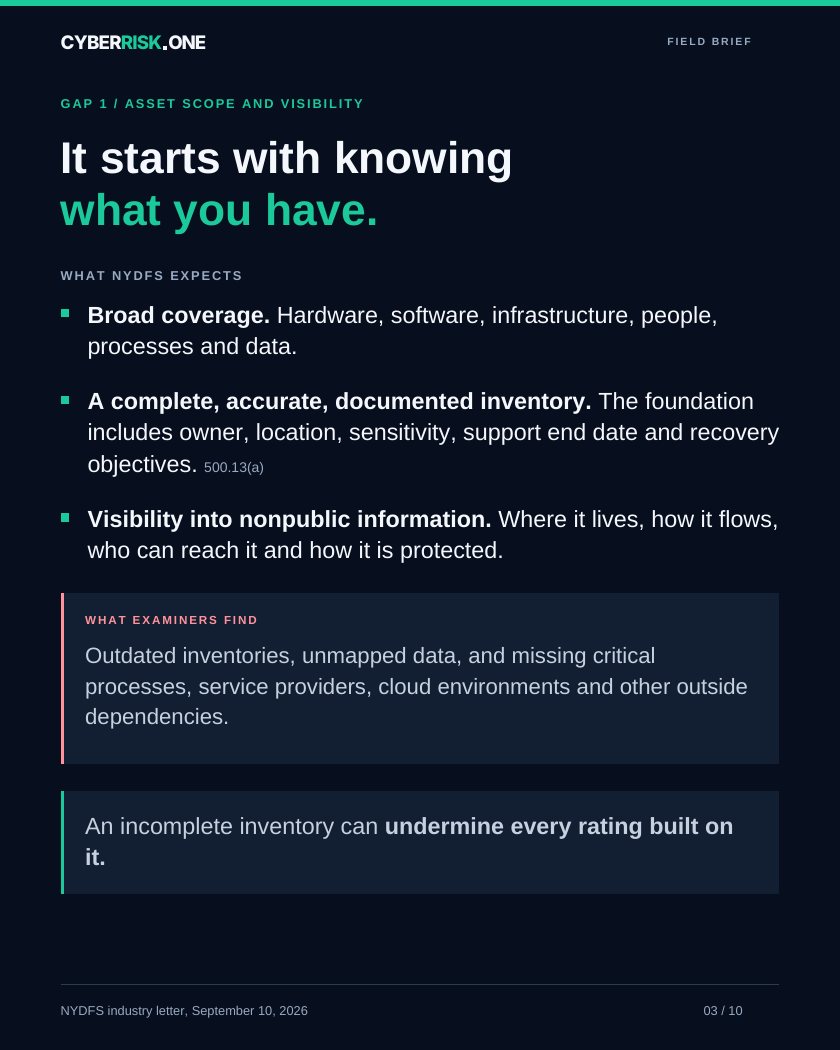
- Asset scope: why an incomplete inventory undermines every rating built on it
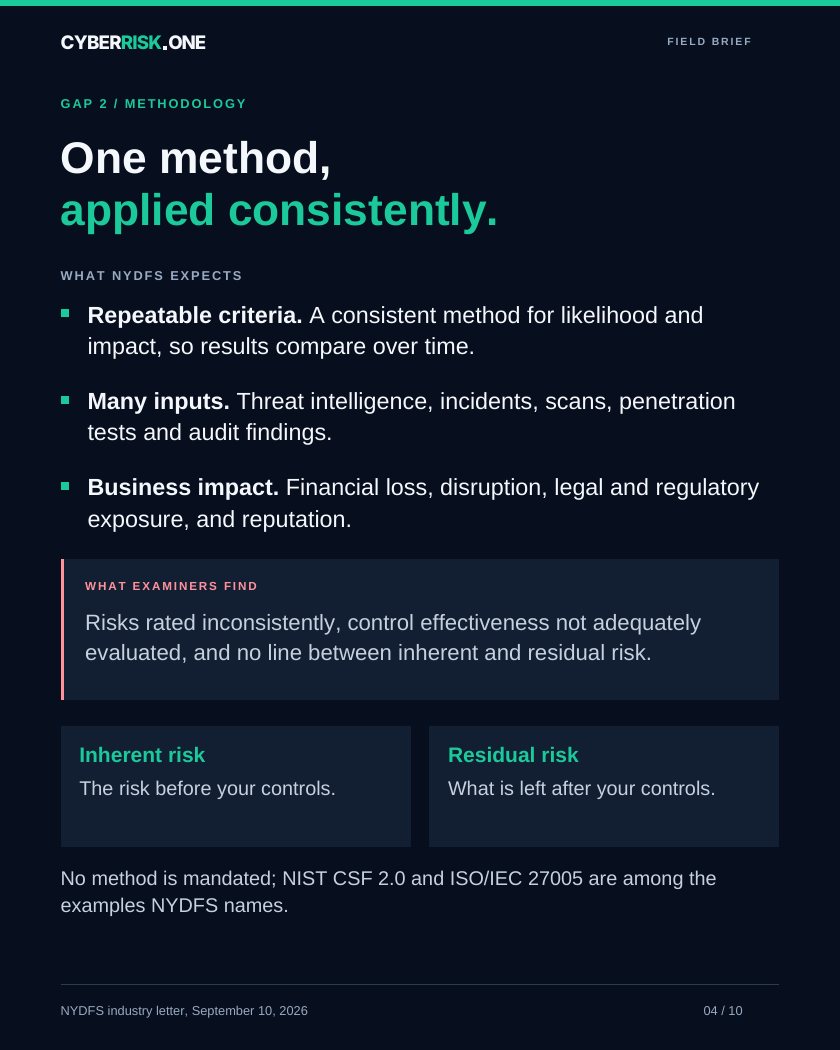
- Methodology: consistent likelihood and impact, and inherent versus residual risk
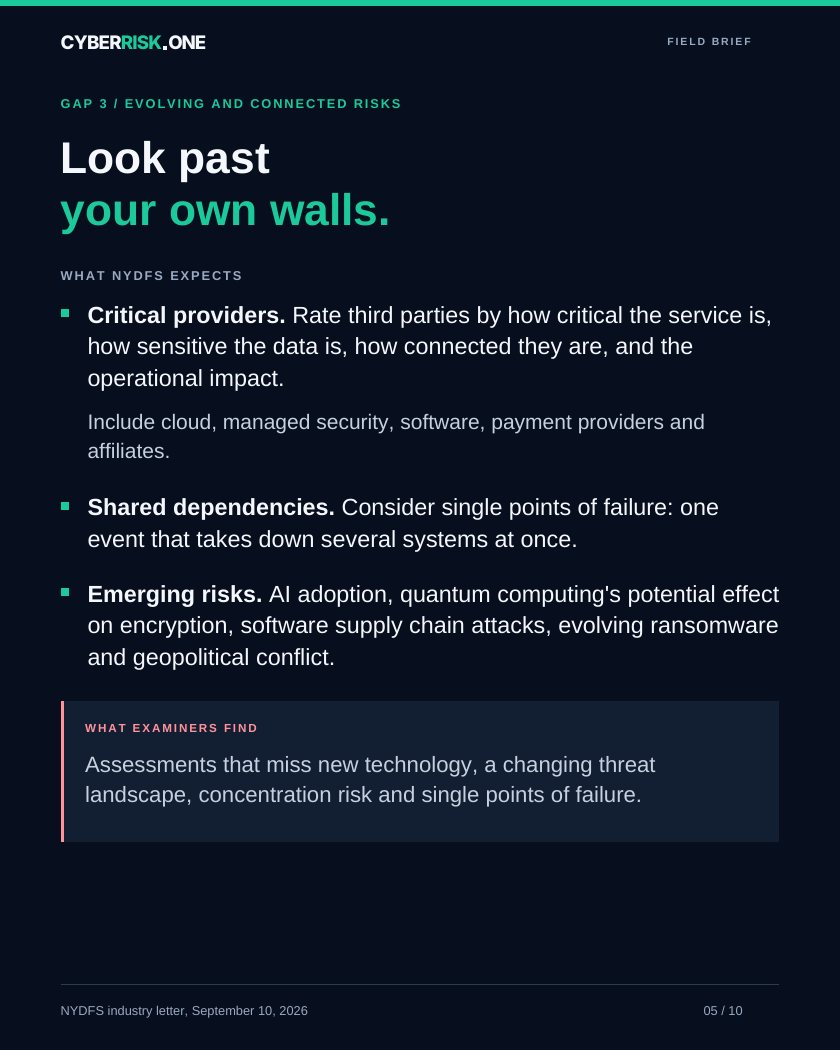
- Evolving and connected risks, including third parties and cloud
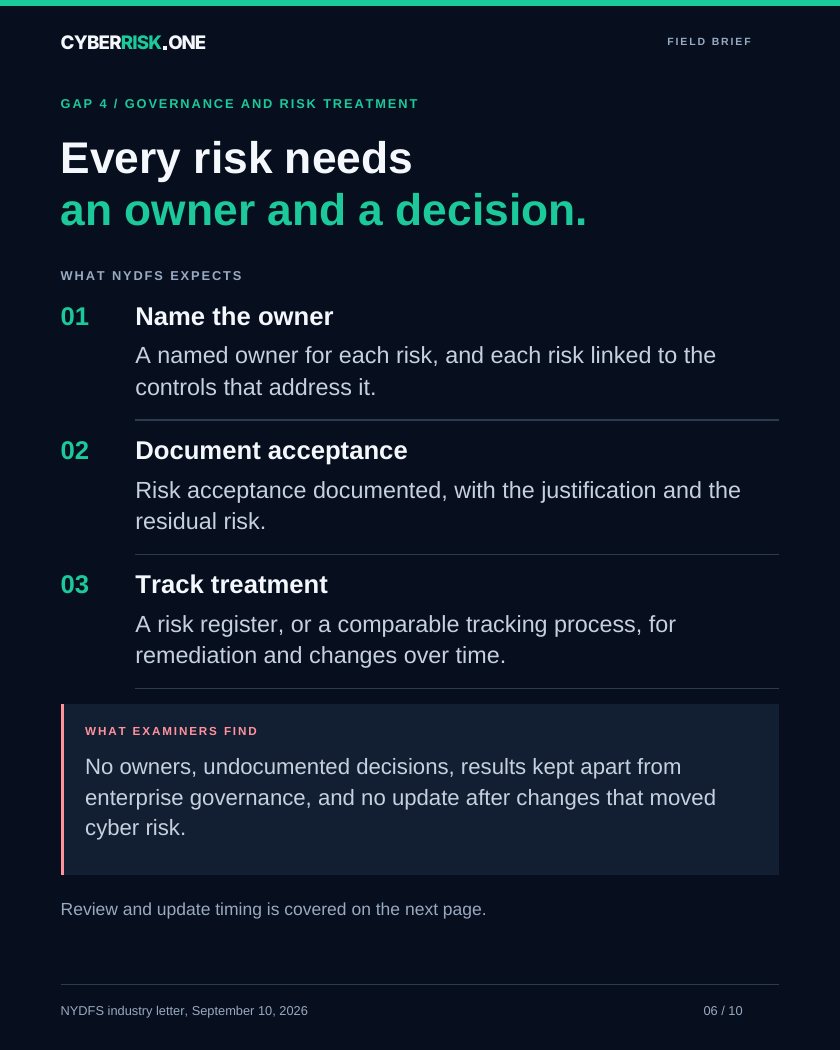
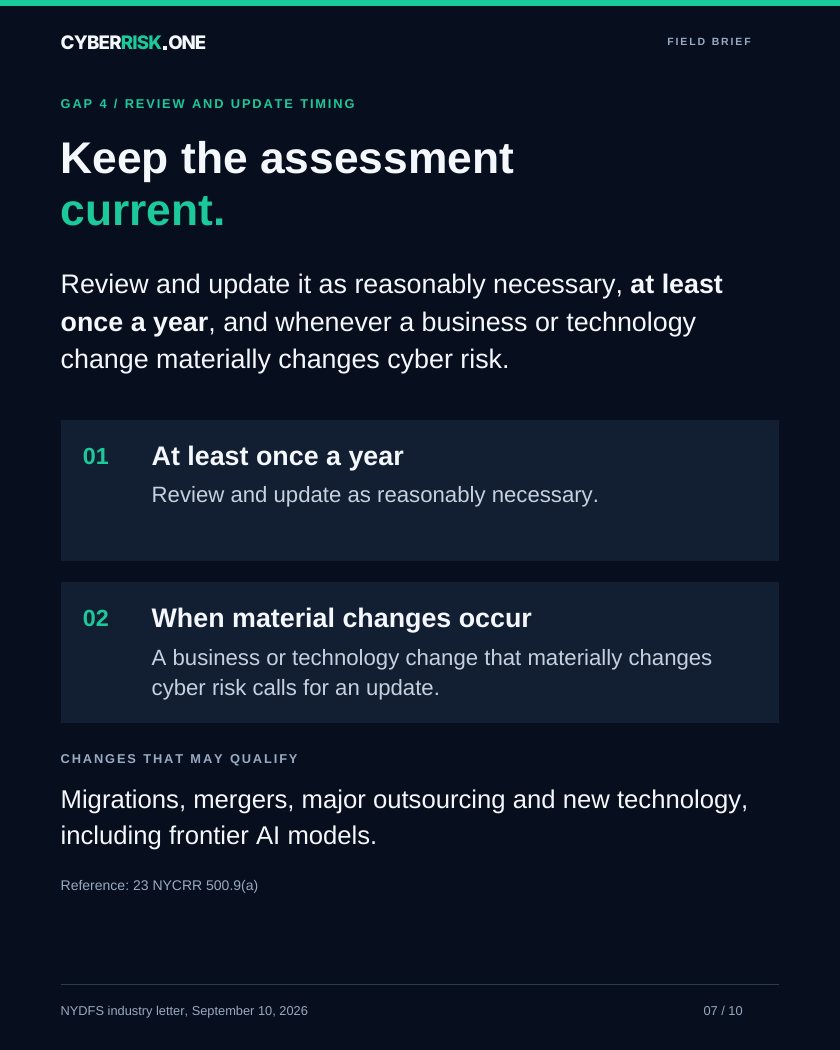
- Governance, risk treatment and how often to review
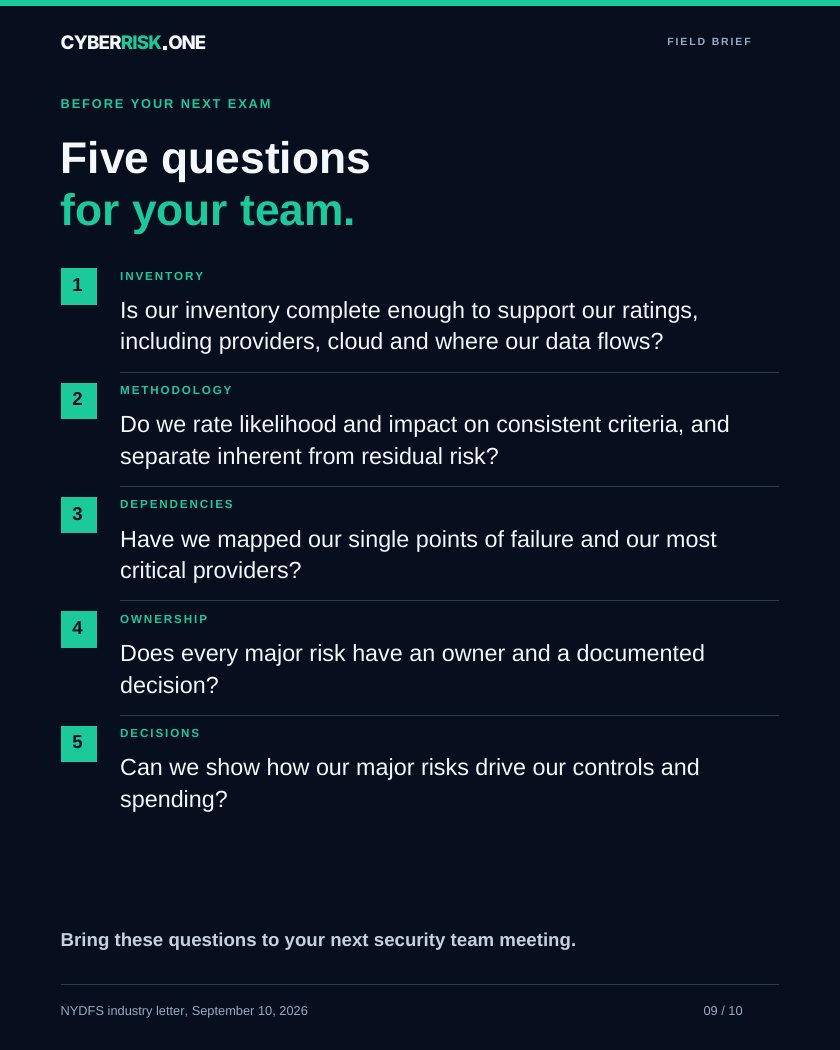
- Five questions to bring to your next security team meeting