◎
Understand your positionNot sure where you stand?
Get clarity on your exposure, understand what matters most, and build a practical plan forward.
Explore assessments →Know what to fix, what to accept, and where your security budget makes the biggest difference.
Practical cybersecurity services, experienced leadership, and clear decisions grounded in your business.
Risk assessmentInstant price estimate→You don't need to know which service to ask for. Start with what's on your mind.
Get clarity on your exposure, understand what matters most, and build a practical plan forward.
Explore assessments →Make the most of what you own, address the gaps that matter, and focus on fixes that stick.
Explore implementation & management →Practical advice for strategy, customer demands, compliance, and complex decisions.
Explore fractional CISO →One specific challenge or a broader program. Each service stands on its own, guided by practical business outcomes.
Understand risk, gaps, and priorities.
Implement changes that improve security.
Make security operational and sustainable.
Experienced advice when it matters.
No mandatory starting point. Our risk methodology strengthens the work, but you can engage any service directly.
High. Medium. Low.
If that's how you describe risk, you're flying blind.
Your business leaders know revenue, operations, customers, and exposure. Your technical teams know systems, threats, and vulnerabilities. We give everyone a common language for making decisions.
The people who understand your needs and scope the work stay responsible for the outcome.
Brian and Dan personally evaluate, scope, and oversee every engagement.
We do the work directly and bring in trusted specialists when the situation calls for them.
We focus budgets on meaningful risk reduction and look for value in tools you already own.
Clear decisions, practical implementation, and improvements your team can sustain.
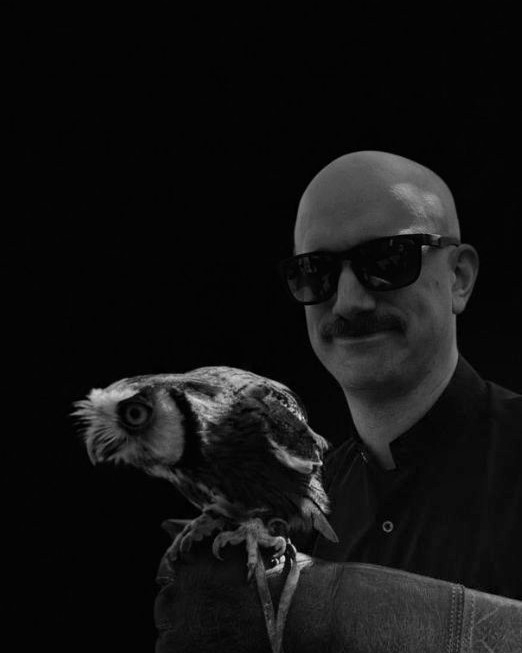
“Cybersecurity isn't complicated. That doesn't mean it's easy.”
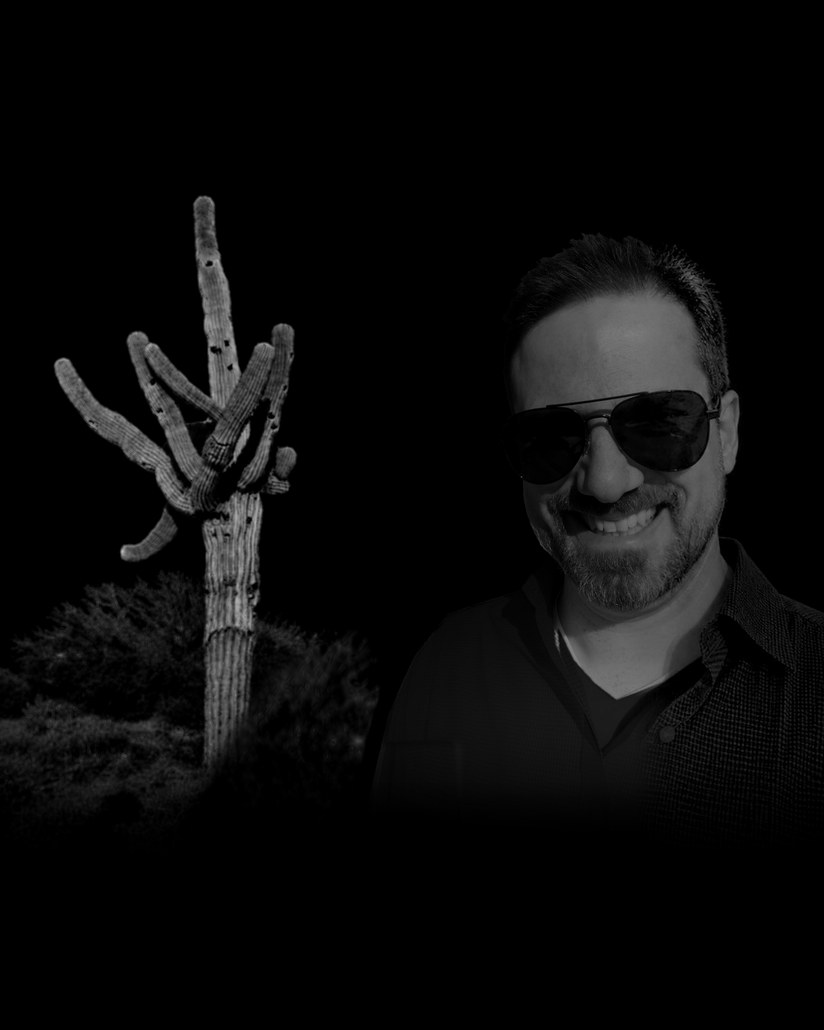
“Security gets a lot easier once it makes sense. I love being there when it does.”
“The best risk assessment I'd experienced.”
Paraphrased client feedback: the CEO then invited CyberRisk One to explain the findings to the wider staff.“Learning we already had enterprise-grade EDR/XDR without needing more licenses was one of the highest-value moments.”
CISO · M365 Security Implementation clientFrom regulated organizations to growing technology businesses, we understand how security requirements intersect with operations.
Also supporting manufacturing, government, nonprofit and legal organizations.
What changed, what it means for your risk, and the questions to ask your team. No unnecessary noise.
Read the latest update ↗One email a month. Practical information you can act on.
Tell us where you are. We'll tell you where we can help.
No obligation. We reply within one business day.